↑
Tangier · --:--
Presented by: Omar BabbaSelected work · 2026Cybersecurity engineer · GRC

OmarBabba

Seeking a GRC final-year internship (PFE) · from February 2027

Open to PFE · Feb 2027
Governance✦Risk management✦ISO/IEC 27001✦Detection engineering✦Incident response✦Threat intelligence✦Governance✦Risk management✦ISO/IEC 27001✦Detection engineering✦Incident response✦Threat intelligence✦
(01) About me

Where governance meets the technical side.

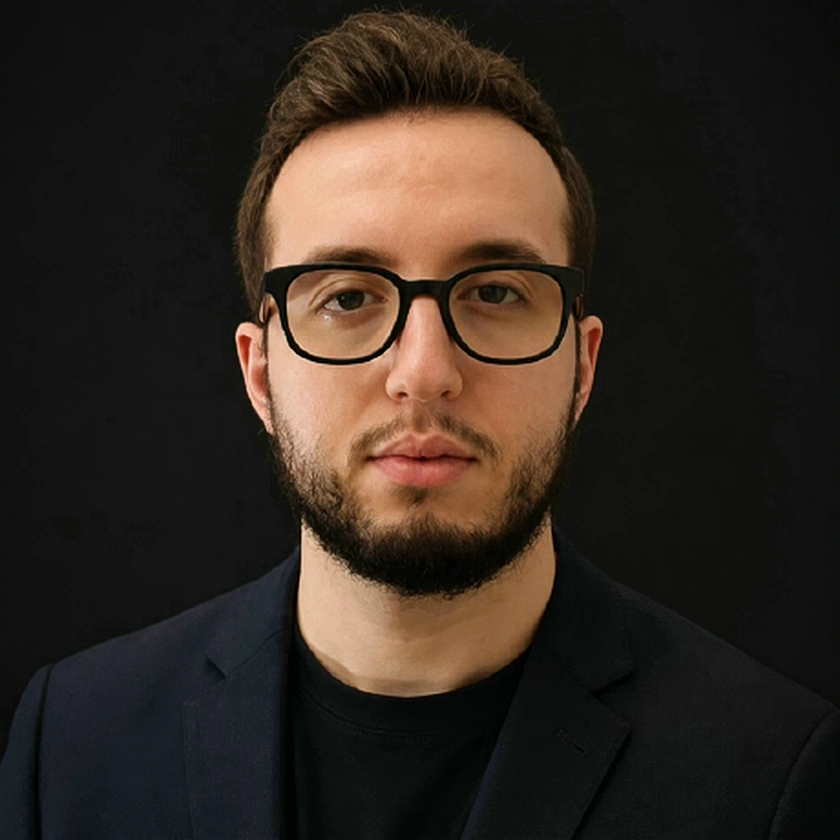
Portrait of Omar Babba
Omar BabbaTangier, Morocco

I’m Omar, in the fifth and final year of my engineering degree at EMSI Tanger, specializing in cybersecurity. I work where governance meets the technical side: I write the controls, then attack them in an isolated lab to see whether they hold.

Two internships at Amendis (Groupe Veolia) took me from security awareness to building an AI-augmented SOC pipeline. Since then I have built governance tooling, detection labs and a monthly threat intelligence report.

“You can only govern what you have seen work — and seen fail.”
  • Arabic · native
  • French · advanced
  • English · advanced
(02) What I do

What I do? (and love doing)

I build security programmes that can be audited and tested: clear controls, maintained risk registers, detections that fire and investigations that close — with the evidence kept for each one.

  • Governance01
  • Risk management02
  • ISO/IEC 2700103
  • Detection engineering04
  • Incident response05
  • Threat intelligence06
(03) Tools

Tools I’m fluent in.

(04) Experience

Where I’ve worked.

Jul — Aug 2026
Amendis Tanger · Groupe Veolia · internship (PFA)

SOC Analyst Intern — AI-Augmented Security Pipeline

  • Designed and deployed an end-to-end AI-augmented SOC pipeline: Wazuh → Shuffle → local Gemma2 (Ollama) → TheHive → Cortex → MISP.
  • Raised MITRE ATT&CK technique-mapping completeness from 40% to 100% on a 25-alert evaluation set, using a local LLM bound to a strict JSON contract.
  • Built and validated six controlled attack scenarios: SSH brute force, suspicious download, encoded PowerShell, lateral movement, C2 beaconing and network recon.
  • Kept routing deterministic and severity-based — AI output stays advisory — with full traceability (RUN_ID, SHA-256 manifests) and 75 automated tests in CI.
  • Built entirely in an isolated lab (VirtualBox, Docker), with no impact on production systems.
Jul — Aug 2025
Amendis Tanger · Groupe Veolia · internship

Cybersecurity Awareness Intern

  • First hands-on exposure to enterprise security within the company's cybersecurity department: InfoSec fundamentals and industry frameworks and bodies of knowledge (ISO 27001, the CISSP domains).
  • Analysed SCADA architecture and its exposure to attacks on critical water and electricity networks.
  • Explored the six modules of the Riot security-awareness platform and took part in a real phishing simulation — click-through fell from 25% to 5% after training.
  • Studied GLPI IT-asset management in an industrial/OT context at the Al Majd site.
2022 — 2027
EMSI Tanger · final year, cybersecurity · graduating 2027

Engineering degree — Computer Science & Networks

  • Fifth and final year of the engineering cycle, specializing in cybersecurity.
  • Coursework in application security, network monitoring, VPNs and intrusion detection — applied in documented, reproducible labs.
(05) Method

How I work.

Whether it is an audit or an incident, the method stays the same.
  1. 01

    Scope

    The assets, the context and the obligations that apply — ISO/IEC 27001, Law 09-08, the DNSSI.

  2. 02

    Assess

    Risks rated in a register someone can actually maintain, with owners and treatment decisions.

  3. 03

    Build

    Decisions turned into controls, detections and playbooks — written down and versioned.

  4. 04

    Test

    My own controls attacked in an isolated lab, so the evidence shows what holds and what fails.

  5. 05

    Report

    Evidence, corrective actions and a management review that closes the loop.

(06) Contents

What you will find inside?

  1. 01Governance, risk & compliance↓
  2. 02SOC & detection engineering↓
  3. 03Incident response & forensics↓
  4. 04Application & AI security↓
  5. 05Threat intelligence↓

Governance

01 — Governance, risk & compliance

Kontrol — an ISO 27001 management system, end to end

Task

Most governance tools stop at a checklist: a ticked control is not linked to the obligation behind it, the evidence that proves it or the risk it reduces.

Solution

A GRC application I built in TypeScript that keeps the whole chain in one place — obligation, control, evidence, finding, risk, signed decision — run on a complete case: Hydria, a fictional water utility.

  • ISMS scope & clauses
  • risk register & treatment
  • multi-framework compliance hub
  • incident & corrective actions
  • management review
  • append-only audit log
Read the case study →

Amane GRC — continuous compliance for Moroccan SMEs

Task

Small Moroccan companies need ISO 27001, Law 09-08 and the DNSSI the most, and can afford a consultant the least.

Solution

A self-hosted platform in French: one programme for three frameworks, checked every few hours by a Windows agent and Microsoft 365, with the Moroccan obligations treated as working tools.

  • continuous control checks
  • EBIOS RM
  • DGSSI incident declarations
  • access reviews
  • public Trust Center
  • tamper-evident activity log
Read the case study →

Detection

02 — SOC & detection engineering

SocForge — one attack, followed from detection to case closure

Task

Prove that a SOC works end to end — not only that alerts fire, but that one attack is followed all the way to a closed case.

Solution

Twelve virtual machines on one PC: Wazuh, OPNsense, Suricata, Zeek, Shuffle, TheHive, Cortex, MISP and Velociraptor. Sixteen real, benign scenarios; on the tracked attack, the attacker is blocked 24 seconds after the alert.

  • 29 detection rules
  • 5 filtered network zones
  • 6-node automated response
  • threat hunting from MISP
  • timed evidence for every step
Read the case study →

PFA-SOC-IA — an AI-augmented SOC pipeline (internship, Amendis)

Task

Use AI to speed up alert triage without letting a model take security decisions.

Solution

A local Gemma2 9B model triages Wazuh detections, then hands off to TheHive, Cortex and MISP, while severity routing stays on deterministic SIEM data. ATT&CK mapping completeness rose from 40% to 100% on a 25-alert set.

  • 7-stage pipeline
  • 6 attack scenarios
  • strict JSON contract
  • RUN_ID & SHA-256 traceability
  • 75 automated tests
Read the case study →

Sysmon + Wazuh — six ATT&CK techniques, verified detections

Task

Show that endpoint telemetry catches a realistic intrusion, not a staged one.

Solution

Sysmon on a real Windows 10 host forwarding to Wazuh 4.12. A causal kill chain — a brute force that succeeds, then a SAM dump as the compromised account — validates 6 custom and 3 stock rules, each confirmed firing.

  • custom detection rules
  • technique-to-rule reference
  • Security Configuration Assessment
  • config-drift findings
Read the case study →

Response

03 — Incident response & forensics

Incident response playbooks — five NIST-aligned runbooks

Task

Make sure any analyst on shift handles an incident the same way, with the same escalation triggers.

Solution

Five NIST SP 800-61 / SANS-aligned runbooks written as decision trees rather than flat checklists, each citing the clause behind every step.

  • six-phase breakdowns
  • decision trees
  • escalation tables
  • evidence checklists
  • two-layer severity model
Read the case study →

Digital forensics — an incident reconstructed to the second

Task

Unusual activity on a Windows workstation: was PowerShell used, was persistence created — and can both be proven from artefacts a third party can verify?

Solution

Acquisition in order of volatility, then reconstruction from disk and registry: three independent sources converge on 17:55:21 UTC, every item hashed and tracked.

  • memory & disk acquisition
  • E01 verification
  • KAPE collection
  • timeline correlation
  • chain of custody
Read the case study →

Malware sandbox — five live samples, analysed safely

Task

Triage suspicious files the way a SOC or DFIR analyst does, without putting anything at risk.

Solution

Static and dynamic analysis of five live samples, including AgentTesla, RedLine and njRAT, on an isolated REMnux machine — network isolation verified, every sample hash-checked.

  • static analysis
  • sandbox behaviour
  • ATT&CK mapping
  • IOCs
  • detection notes
Read the case study →

AppSec

04 — Application & AI security

Web app playground — vulnerable vs hardened, side by side

Task

A pentest PDF asks the reader to trust a severity rating. Show the exploit and the fix instead.

Solution

A dual-mode gateway in front of the same application: the same OWASP Top 10 exploit dumps the users table in vulnerable mode and returns 403 in hardened mode, naming the defence that stopped it.

  • vulnerable vs hardened runs
  • ZAP automation
  • SIEM detection layer
  • Jest & fuzzing coverage
Read the case study →

LLM security lab — the OWASP Top 10 for LLMs, attacked and fixed

Task

Write-ups on LLM risks stay abstract. What does each risk look like in code — and what change closes it?

Solution

One RAG/agent system built twice, wide open and hardened, answering the same requests, so every fix is shown against the exact attack it stops.

  • 86 pytest tests
  • 21-check attack benchmark
  • 72 fuzzing cases
  • sandboxed tools
  • capability-based RBAC
Read the case study →